You need the thing built, not advised on
DevelopmentWe write the software. In house, on our own stack, with a short supply chain and the smallest blast radius we can design into it. You own what we build.
The AI security review, in full →
If your company has already approved an AI tool, the missing piece is usually someone setting it up on the work a person actually does. That's the work we do: setup on one real workflow, starting with project status and risk reports, training for the person who owns it, a reviewer on every result, and a subscription that keeps the setup and its rules current as your company changes. Each quote comes from the value of the workflow being handed off.
Our specialty is use-case identification: vision-first, working backwards from where the business should be to the repeated work worth changing now.
Setup, training, a reviewer on every result, a measured before and after, and a short written pack for IT whenever something new is added. Personal use inside tools your company already approved, with nothing new installed, connected or shared, needs no IT review.
We are built for the people who own AI adoption inside large companies, and for the trainers and consultants who work alongside them. The security review is the same for any size of company.
These are not five products to choose between. They are the five shapes the work usually takes, and most engagements use more than one.
We write the software. In house, on our own stack, with a short supply chain and the smallest blast radius we can design into it. You own what we build.
One repeated task, handled end to end, with a review gate that stays yours. You set the rules, and nothing goes out unless it passes them.
We check agent behaviour against a fixed expected outcome, graded the same way every time, and never let an agent grade its own work. Where we have no measured baseline yet, the result reads unmeasured rather than pass.
Use-case identification, vision first, working backwards from where the business should be to the repeated work worth changing now.
People practice on the system they will keep using, on their own work, and leave with a proof note their manager can read.
The review is a separate engagement from the setup above. Most new software now ships with AI in the loop. Supabase alone reports that coding agents launch the majority of its databases, millions per month, by its CEO's own count. Once that software touches real money, customer records, or the public, somebody has to keep it safe, and almost nobody is assigned to. That is where the review starts.
The same engine we point at our own repositories, including the one this website lives in. Every check you get has been run on us first.
More than 35 static-analysis rules across Go, JavaScript, TypeScript and Python, plus credential-storage rules for Swift. No model call anywhere in the scan path, and the exact rule definitions that graded your code are hashed into your report so they can be re-run and checked.
The packages your project pins, checked against the public OSV vulnerability database. Anything we could not reach is listed as unmeasured, never as clean.
Keys, tokens, and credentials left in the tree where an agent can read them.
What your agents were actually told to do, read as source rather than taken on trust.
Whether AI answer tools describe you correctly when a buyer asks about you.
It is reported as unmeasured and held apart from a clean result. Two of the five engines exit quietly when they have skipped the work, so a green report you cannot trust is the failure we designed against first.
A written capability map, a live walkthrough where you watch your own AI act, and, on request, a signed record binding the report to the exact list of checks that ran.
You already know what those hours cost you, to the hour, better than any calculator we could put on this page. So here is our side of it instead.
The first engagement is a short pilot on one person's status and risk reports, six weeks long (a baseline week, a setup week, then four measured weeks), with accepted work, rework and checking time as the pass line, and you decide on the subscription after you read the numbers. The subscription keeps your rules current through a dated rules file you review and accept inside your approved tool, and anything that would widen what an agent can reach goes through the short IT pack first. The price has three parts: a setup fee for the pilot, a subscription after it, and model usage that runs on your approved AI on a budget we agree with you. No figures are published, and each part is agreed on the free call before any work starts. The setup fee for the pilot is fixed and agreed before we start, and the first week is free, so you can stop after it if it isn't a fit. We reply within one business day, and we aim for two to four hours. We never assume a subscription you already have covers model usage. The before and after is measured for the person first, shared with their team only with their say, and never used for performance review. The security review stays one fixed scope at one fixed fee, and fixing what it finds is quoted per client after you have read it.
Setup on one person's real workflow, training for the person who owns it, and a subscription that keeps the agents and their rules current. It starts as a short pilot with a setup fee, then a subscription, and model usage runs on your company's approved AI on a budget we set together. No figures are published. The security review is separate, at one fixed fee given on the free call.
A freelancer builds it and leaves. The next change, the next fix, and the maintenance are each a new quote, and nobody carries the context between them.
Your own hours at your own loaded rate, which you know better than we do.
An AI system runs each of these. You keep the review gate and set the rules, so nothing goes out unless it passes them.
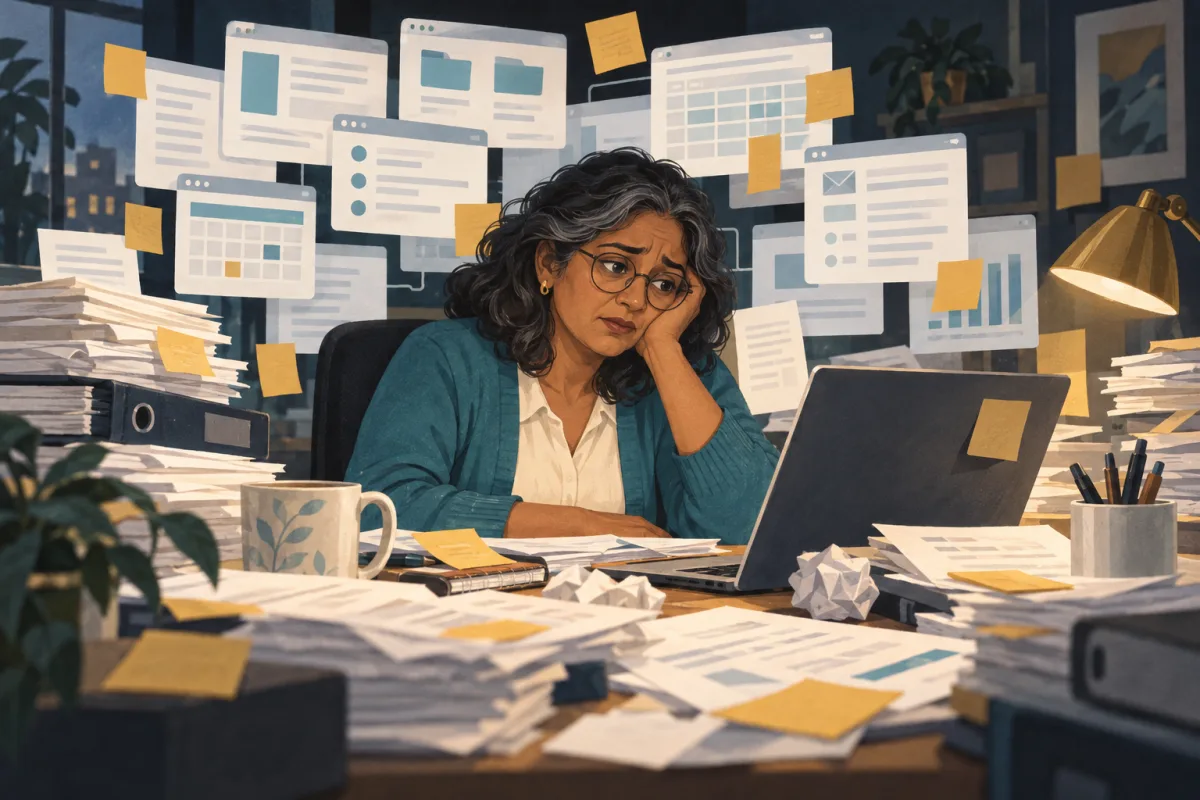
You chase updates across six tools.
You copy them into a doc and guess the risks from memory.
Next week, you start over.
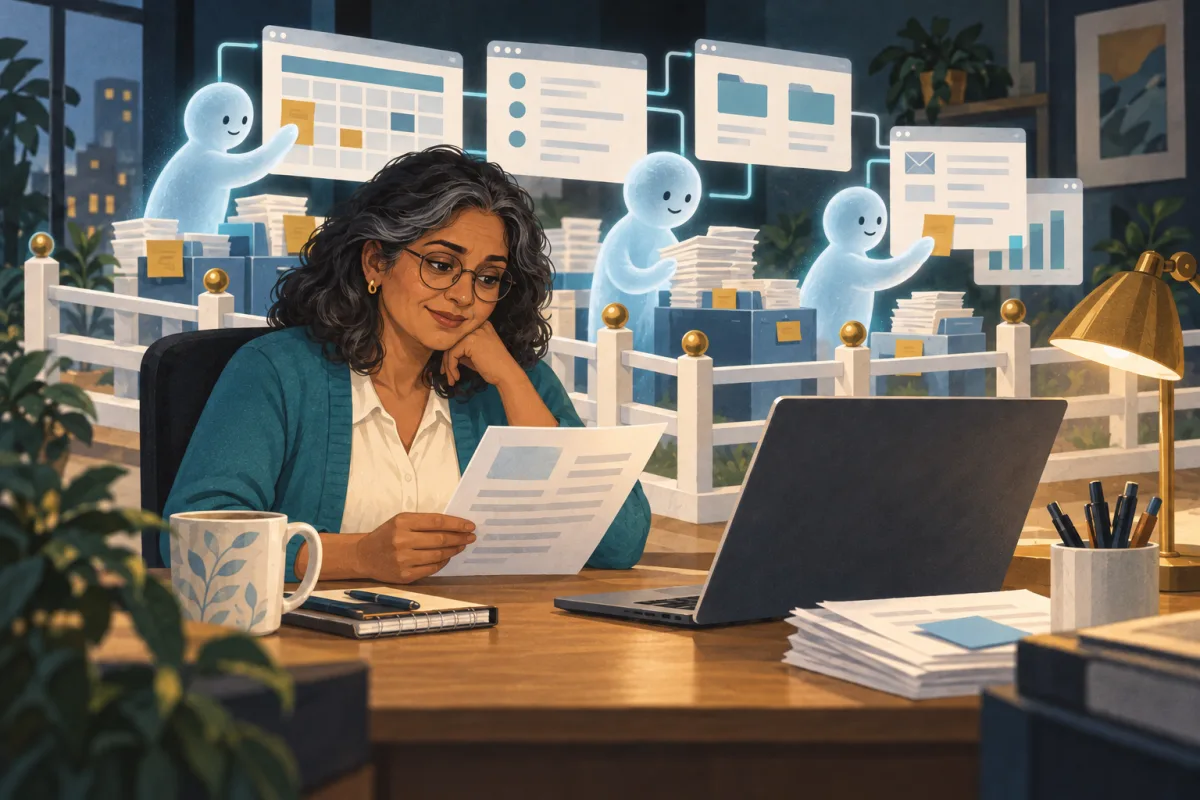
Your agents gather the updates from the tools you already use.
A separate reviewer agent checks the draft against its sources before you see it.
You read it, fix what's off, and send it yourself.
This is what the six-week pilot sets up. Your first week is free.
Recorded run. Every date is real. This is us running our own method on ourselves.
STEP 1 OF 5
2026-06-16
Our own system queried five answer surfaces about us: ChatGPT, Claude, Perplexity, Google AI Overviews, Google Knowledge Graph.
Done-with-you AI adoption: we find the first repeated task worth changing, build it in house, train the team on their own work, and leave receipts. Your documents, decks, and reports generate themselves in your own style, and the tools you keep stay connected. It starts with a free 30-minute call.
A course or a few tools
You learn the ideas and try a prompt or two.
No working system
The new way of working never lands inside your own business.
Done-with-you build
Someone builds the system with you and trains the team.
Bring a task, a question, or just curiosity. We show you where AI fits, where it does not, the risks, and a first move. If it looks like we can help, you get a link to book a free 30-minute call. No sales script and no obligation. If we are not the right fit, we will say so and point you somewhere better.
The booking link opens once the business and task are filled. It goes straight to a calendar, so there is no new backend and no marketing list.
We write up what we learn as we build. Roughly monthly, and you can leave whenever you want.
Mailchimp emails you to confirm before adding you. We never sell your address.
We set up the AI your company already approved on one person's real work, starting with project status and risk reports, with a reviewer on every result and a measured before and after, and then we do the same with the next person on their team. The security review of what your AI can already do on its own is a separate engagement.
Training is tied to the work itself. People practice on the system they will keep using and leave with a proof note their manager can read.
Yes, as part of training we design and build the onboarding system end to end: the curriculum, the flows, the pages, and the backend behind them. That covers new hires ramping on real work and the customers or members you onboard into your own product or community.
We do not automate a whole business at once. We choose one task, build for it, review it, teach it, and only then widen the work.
Both. Setup and training install it, and a subscription keeps the agents and their rules current as your company changes, and where a setup adds tools or connectors, GuardClaw is available as the guard layer for them.
Yes, when the exact tool or code can be checked. If it is public we compare it from source. Otherwise we verify the real thing before we advise.
Yes. Trainers and consultants who already work inside companies can bring us in on a client's workflow, and the setup, the check on every result and the measured before and after work the same way. A partner who brings us in gets a referral fee on the setup, and a partner who also delivers the training shares in the first year of the subscription. Terms are agreed on a call.
The first setup is a six-week pilot on one person's weekly status and risk reports, small enough to approve alone and measured before anyone else commits.
Someone who sets it up on the real work, trains the person who owns it, and stays to keep it current. That is what we do, and it starts with a free 30-minute call.